Senior judgment,
without the complexity tax.
Apogee Defense provides cybersecurity advisory for leadership teams that need clarity, structure, and experienced judgment — not another vendor relationship to manage.
The gap between obligation and capacity keeps widening.
Leadership teams are being asked harder questions about risk, compliance, customer trust, cyber insurance, sensitive data, and AI-enabled workflows. At the same time, most of these companies are nowhere near ready to hire a full-time CISO or stand up an internal security team.
Apogee Defense exists to close that gap: senior guidance for organizations that need clear thinking, practical priorities, and a path from assessment to execution.
How we work.
We don't open by pushing tools. We open by understanding the business.
01Business first
Security should support the organization's goals rather than manufacture friction. Decisions get tied to business risk, customer trust, operational resilience, and what can actually be executed.
02Clear priorities
No organization can fix everything at once. The work is deciding which risks matter most, what needs attention now, and what can be sequenced later.
03Practical roadmaps
A roadmap is only useful if someone can act on it. Ours produce next steps, named ownership, and decision points.
04Framework-aware, not checkbox-driven
NIST 800-171, DFARS 252.204-7012, and CMMC 2.0 matter. Paperwork for its own sake does not. The objective is defensible security aligned to real business needs.
05Secure innovation
AI and automation create real value, but sensitive workflows need governance, security boundaries, and human review. We help clients adopt those capabilities carefully and describe their maturity honestly.
Led by CISSP, CISM, and C|CISO-certified leadership.
That experience is applied to decisions about risk, compliance, governance, program maturity, and future security investment. The work stays focused on what leadership needs to know:
- Where are we exposed?
- What matters most?
- What does the business need to decide?
- What should we do in the next 30, 60, and 90 days?
- What support do we need after that?
What this is not.
Clarity cuts both ways. Here is what we do not do, so you can rule us out quickly if we are the wrong fit.
- Managed IT or helpdesk services
- Tool resale — we hold no vendor partnerships and take no referral fees
- Guaranteed certification outcomes or formal audit substitution
- Penetration testing or offensive security
- A promise that risk can be eliminated
- AI system development or implementation — we advise on the build, we don't do it
Where this is headed.
Apogee Defense leads with fractional CISO and cybersecurity advisory work. The practice is deepening in one direction in particular: helping leadership make security decisions about AI and automation before a build starts, while the requirements are still cheap to change.
That work is advisory and it stays advisory. We do not build, code, or implement the systems, we hold no vendor partnerships, and we have no AI product of our own to point anyone toward. What we bring is the judgment to say what a system must not touch, what has to be reviewed by a person, and what has to be provable afterward.
The long-term direction is straightforward: help organizations make better security decisions today, and be genuinely useful on the harder decisions that arrive as more of the business runs on systems nobody scoped carefully.
What the work has looked like.
Four engagements are described in detail on the representative experience page — what triggered the call, what was delivered, what changed, and where our role stopped. No client is named, and the anonymization rules are stated on the page rather than left for you to infer.
Who you actually work with.
Engagements are led personally. You are not handed to a delivery team after the sales call, because there isn't one.
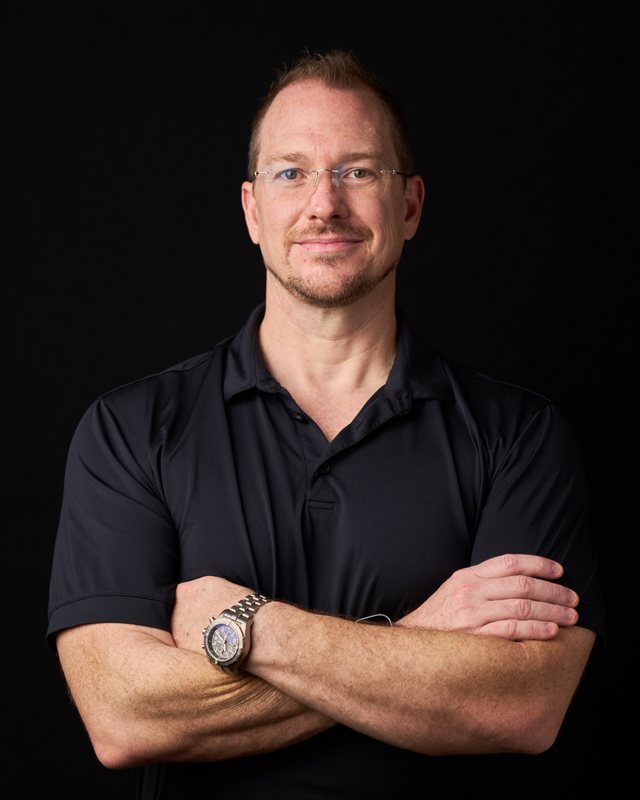
Chris Robertson
Principal & Lead Fractional CISO
Chris Robertson leads Apogee Defense’s Executive Advisory practice, helping organizations translate complex cybersecurity, regulatory, and operational requirements into practical programs that support resilience and growth. He provides fractional CISO leadership across cybersecurity strategy, CMMC and NIST alignment, security architecture, and operating-model development, while also advising on security architecture for agentic AI systems, where controls have to be embedded throughout the development lifecycle. Chris brings more than 20 years of experience across technology, cybersecurity, business operations, professional services, sales, analytics, and organizational transformation.
Austin, Texas.
- Address
- 14425 Falcon Head Blvd, Suite E100
Austin, TX 78738 - Phone
- 512-994-4441
- @apogeedefense
Get a clearer starting point.
Thirty minutes to see whether an assessment is the right next move. If it isn't, we'll tell you that on the call.